Section 1 is the Cyber Security department of PS 1978 Limited.
We conduct targeted audits and vulnerability research on enterprise systems to isolate critical flaws before they compromise business operations.
The longest forever-day in consumer mobile history.
Section 1 conducts vulnerability research on products used by millions. Every finding is documented, verified, and published through coordinated disclosure.
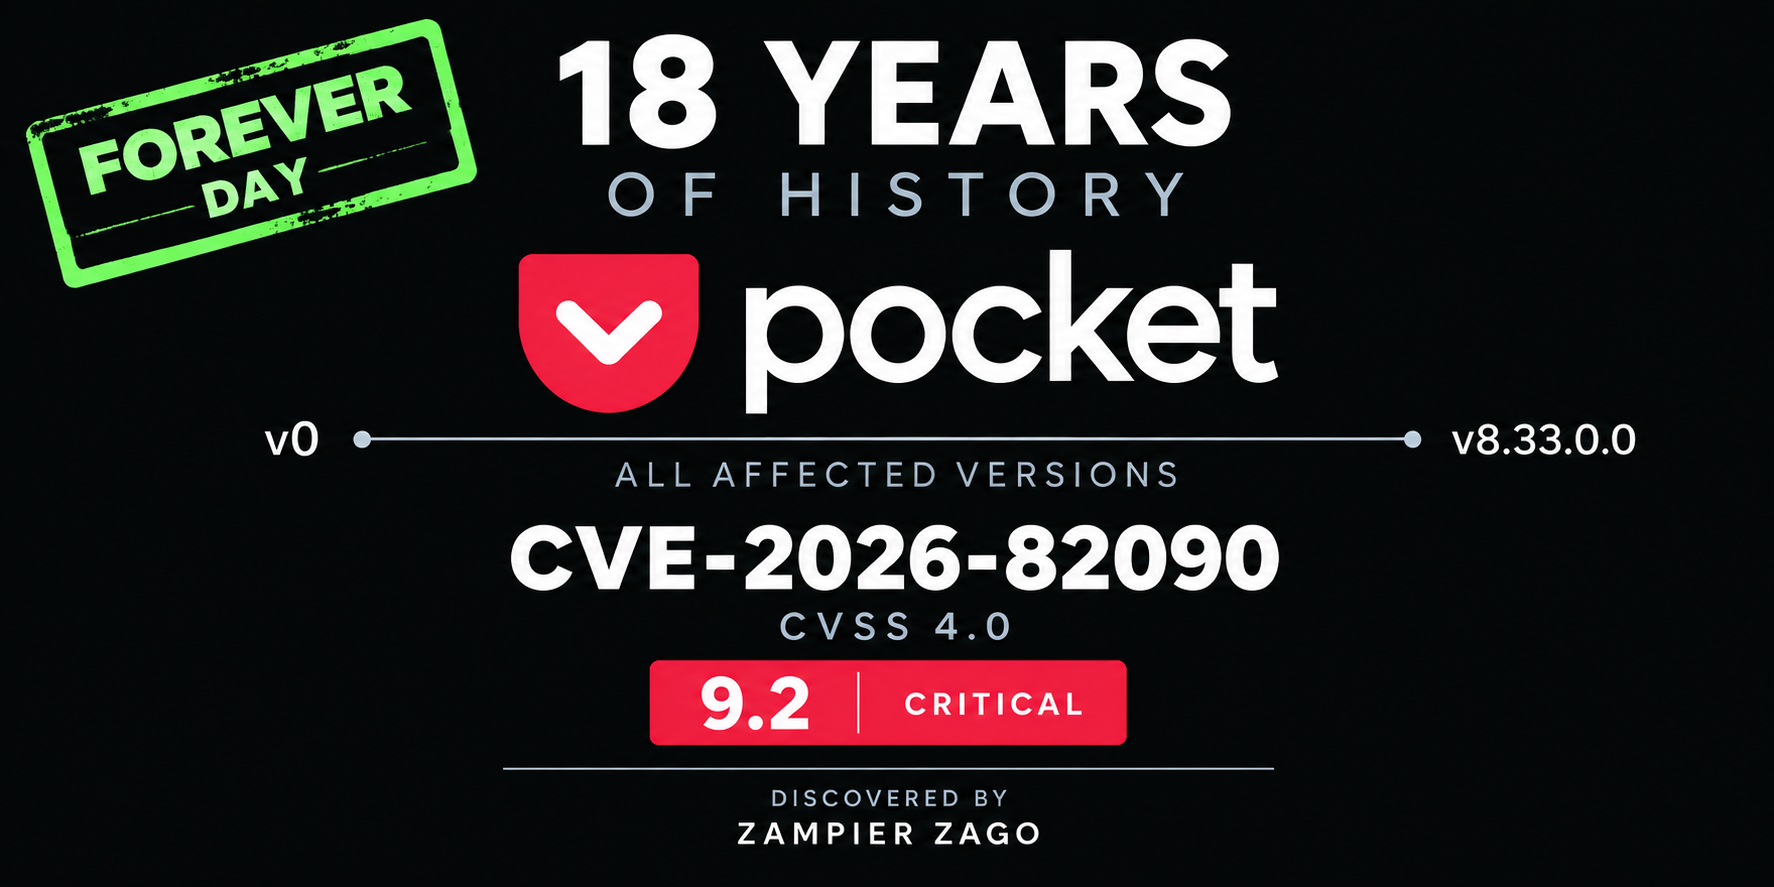
Stored XSS via user-controlled HTML in WebView. All versions from v0 to v8.33.0.0. Thirteen years unpatched.
9.2 · CriticalArbitrary HTML and JavaScript execution in WebView. No sanitization on archived content.
8.8 · HighHTML injection in article rendering. Stored persistently across user collections.
7.1 · HighThe Pocket forever-day
A critical vulnerability present from the first version to the last, across every platform, for the entire life of the product.
First identified in 2012 on an iPhone 4. Formally reported in 2021. Rejected by Mozilla as out of scope in July 2024.
Published by MITRE as CVE-2026-82090 on August 28, 2026 — CVSS 4.0: 9.2 Critical. Every version of Pocket ever released, from v0 to v8.33.0.0, on every platform, carried the same stored XSS through the WebView JavaScript bridge.
Pocket was used by tens of millions of people across 18 years of product history. The vulnerability was never patched. The product was shut down with the flaw still present.
On the basis of publicly indexed records across CVE, NVD, CISA, and web archives, CVE-2026-82090 is the only critical forever-day (CVSS ≥ 9.0) documented on a standalone consumer mobile application.
Every other forever-day with CVSS ≥ 9.0 found on a mobile app is a companion for external hardware — a projector remote, a dashcam viewer, a garden robot controller — with product lifecycles of two to five years and user bases smaller by orders of magnitude.
Documented forever-days on mobile apps (CVSS ≥ 9.0)
| CVE | Product | Type | Lifecycle | Severity |
|---|---|---|---|---|
| CVE-2026-82090 | Pocket (Mozilla) | Consumer app | 18 years · tens of millions of users | 9.2 Critical |
| CVE-2021-43717 | Epson iProjection | Projector companion | ~4 years · niche | Critical |
| CVE-2025-30137 | G-Net GNET | Dashcam companion | ~3 years · minimal | Critical |
| CVE-2026-10557 | Yarbo | Garden robot companion | ~2 years · minimal | Critical |
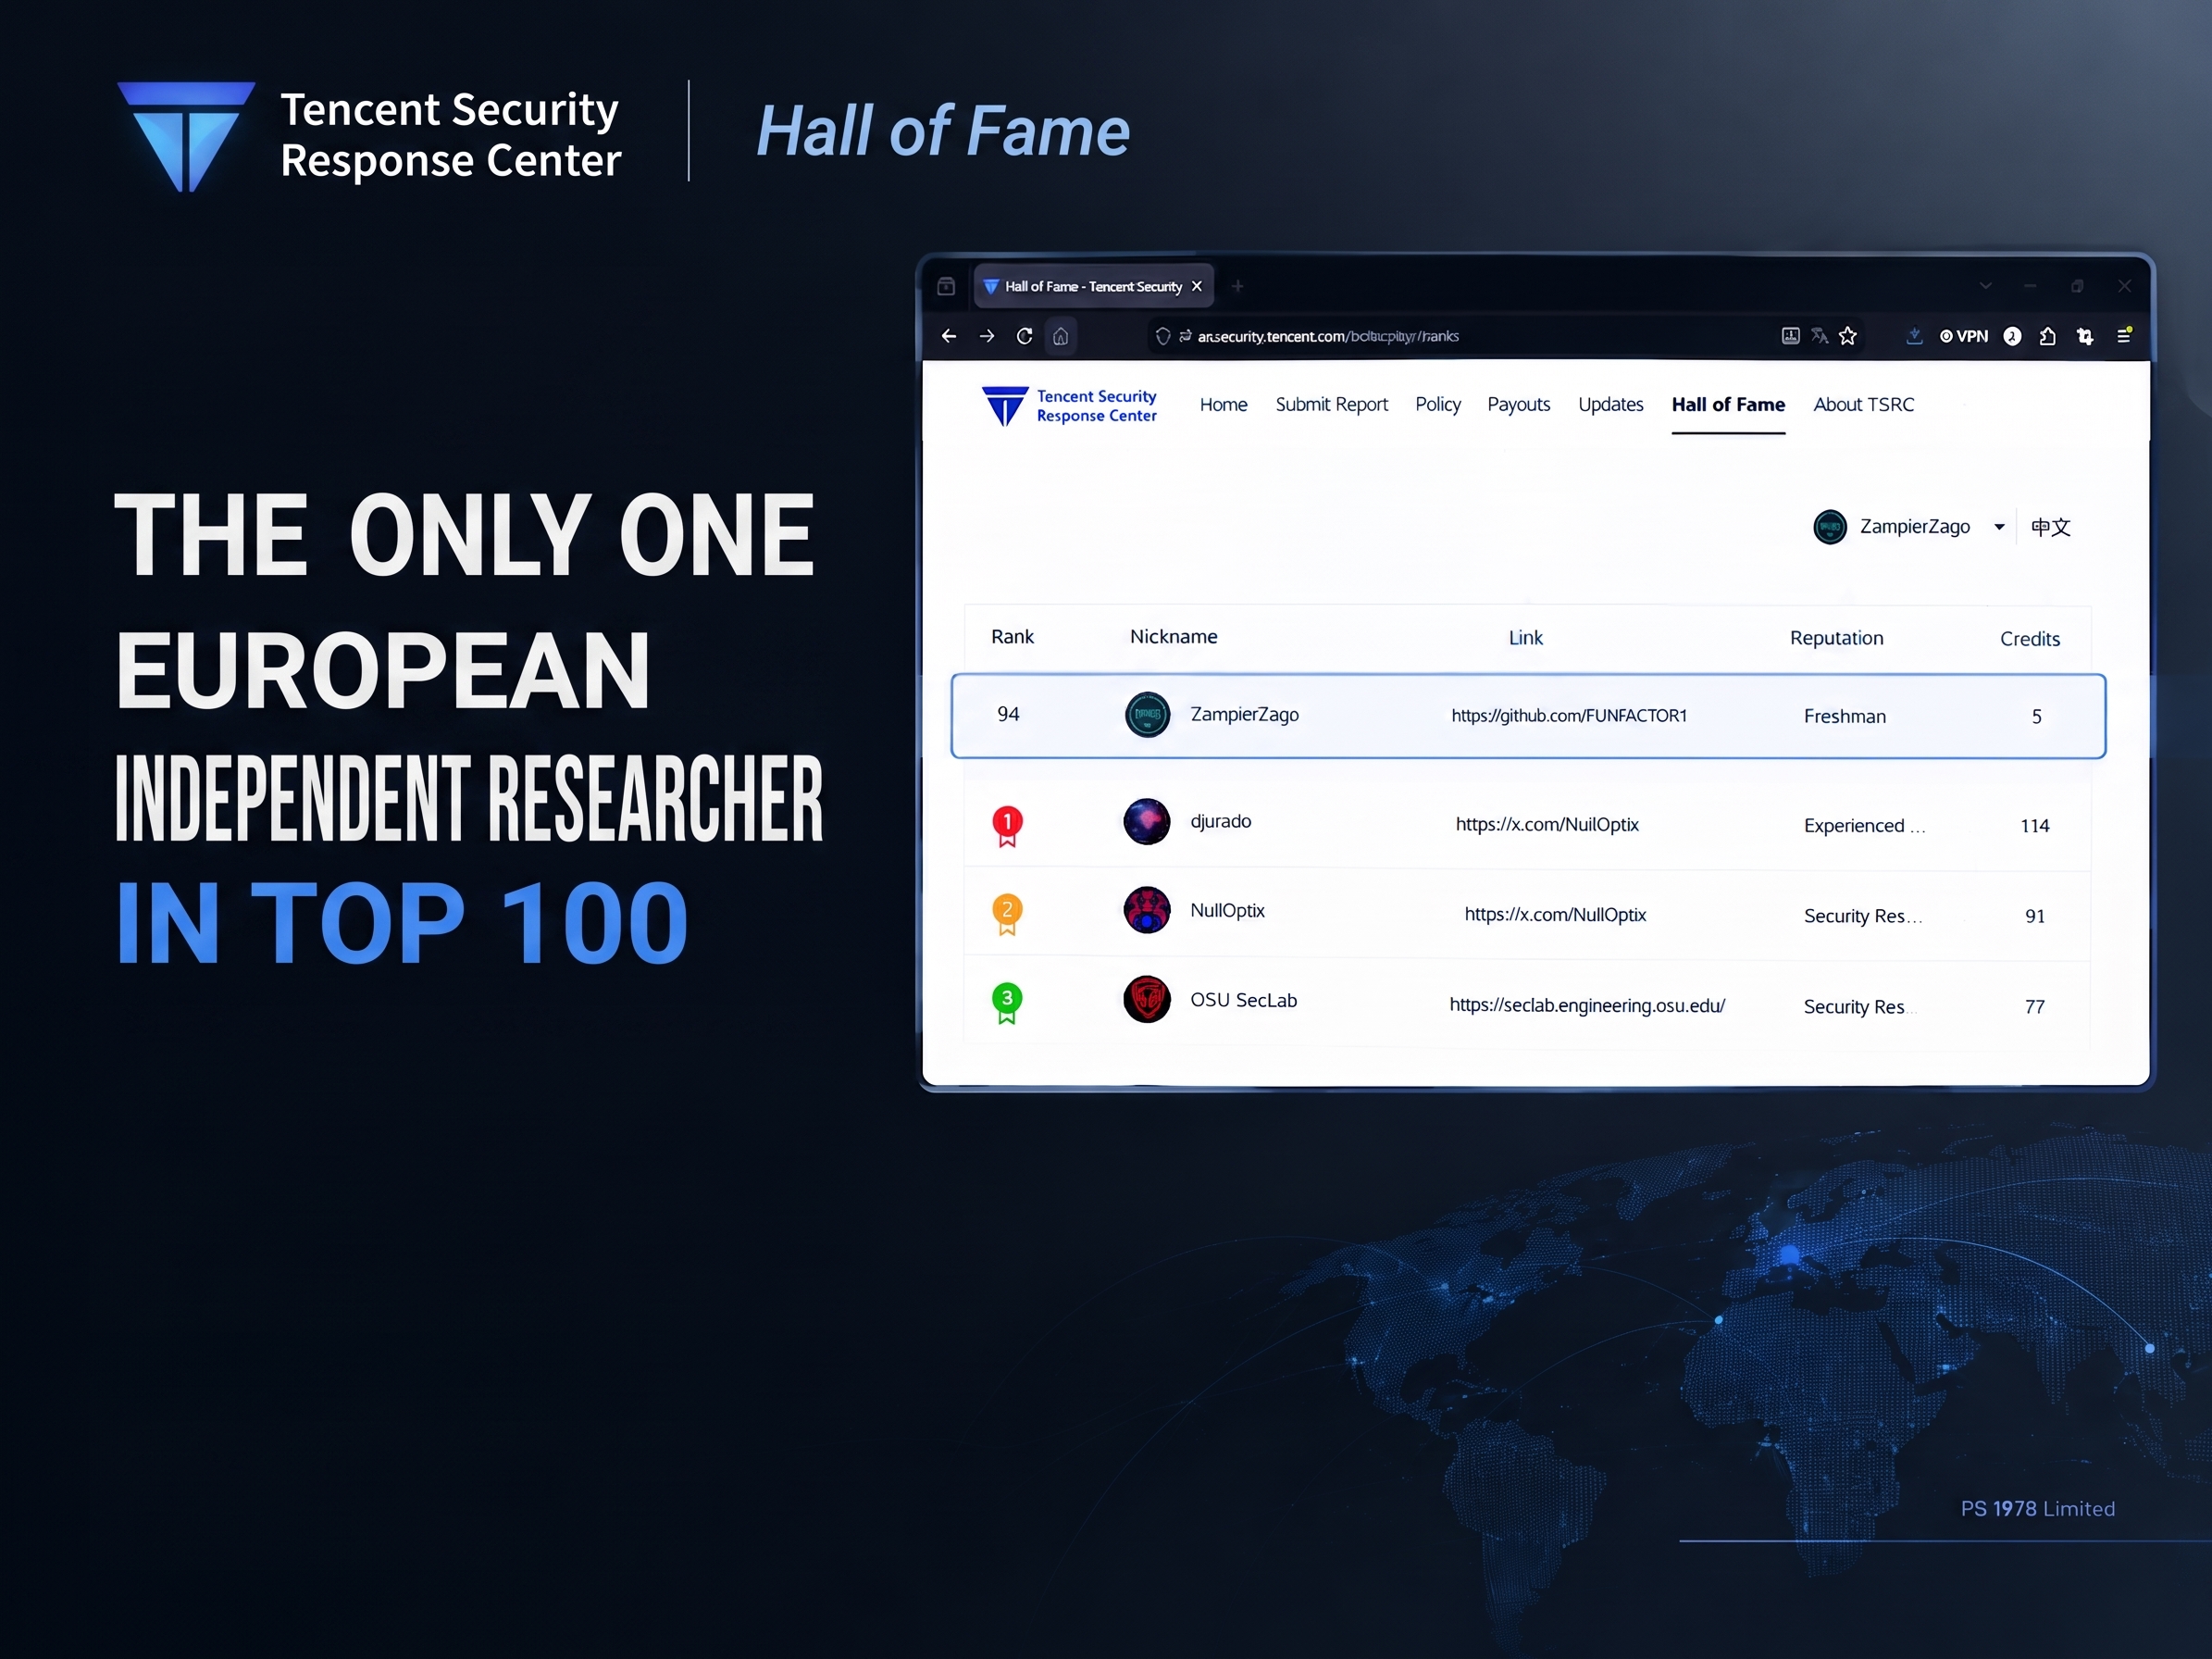
Tencent Security Response Center
Top 100 in the Tencent SRC Hall of Fame. The only European independent researcher in the ranking — every other European entry operates with a team.
Vulnerability accepted on WeChat with credits published. Technical report covering six distinct code paths across WeChat Web, verified independently on five separate attack surfaces.
Capabilities
Security research, audit, and coordinated disclosure as a service.
Attack surfaces
Android · iOS · Web applications · Desktop · WebView · REST API · AI agents and LLM integrations
Vulnerability classes
Stored and DOM-based XSS · JavaScript bridge escalation · CSRF chains · Prompt injection · Exported component misconfiguration · Command injection · Privacy and GDPR compliance
Stack
JavaScript (jQuery, AngularJS, React Native, Webpack) · Java and Kotlin · Objective-C · Python and Django · PHP · C/C++ native libraries · Smali/DEX reverse engineering
Deliverables
Technical report with reproducible evidence chain · Working PoC on controlled endpoints · Patch proposal · CVE advisory draft · GDPR compliance dossier
Engagement
One-shot security audit · Disclosure-in-progress consulting · Periodic retainer · On-call
Methodology
Static analysis on decompiled source. Dynamic verification on researcher-owned devices. Every finding timestamped with eIDAS-certified legal deposit before vendor contact. Full coordinated disclosure cycle through MITRE, CERT/CC, CISA, and vendor-specific platforms.